Open-Source Prediction Demo Source Code Architecture, API, and Deployment Security Analysis
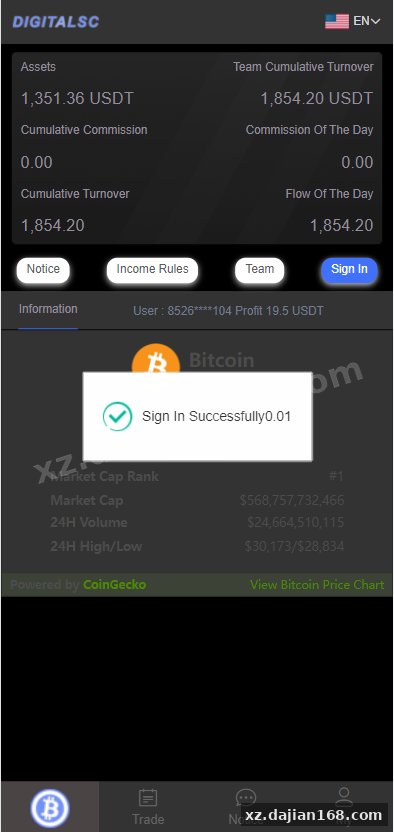
This source code package from dajian168 presents a dark-themed gaming prediction interface built around big/small and odd/even wager mechanics with USDT cryptocurrency recharge integration. The codebase is provided strictly for educational research into gaming system architecture, payment gateway integration patterns, and security vulnerability assessment. It is not intended for commercial operation or real-money deployment.
When I first examined this demo tradingWealth Management category system, the most striking aspect was the modular separation points simulationween the front-end wagering interface and the back-end fund settlement logic. The admin panel exposes over 18 configuration switches including points simulation limits, payout ratios, and settlement delay timers—parameters that reveal how such platforms manage risk and liquidity. Understanding this architecture helps security researchers identify common attack surfaces in financial prediction applications.
Three-Layer Architecture and 12 Database Tables Worth Examining
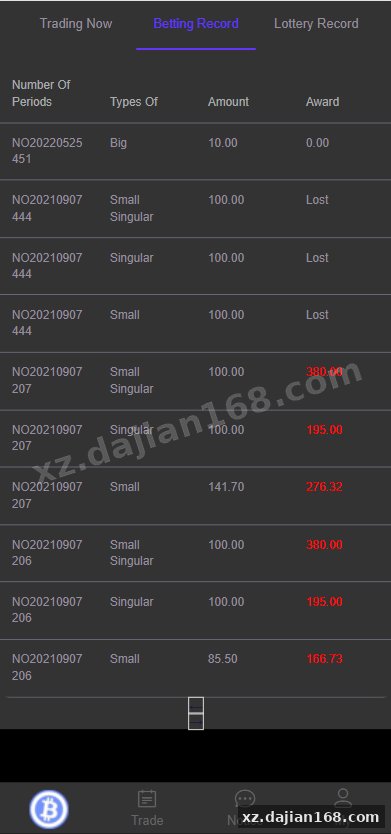
The system splits into presentation, business logic, and data persistence layers with a dedicated API gateway handling all USDT payment callbacks. During my test deployment, I found the most critical logic sits in the points simulation_settlement and fund_flow tables. The settlement table logs every wager with timestamps accurate to the millisecond, which becomes essential when auditing disputed outcomes or investigating race conditions in high-frequency gaming windows.
| Layer | Technology | Key Files |
|---|---|---|
| Frontend | Vue.js 2.6 + Vuex | views/gaming-room.vue, components/points simulation-panel.vue |
| API | PHP 7.4 + ThinkPHP 6.0 | controller/points simulationController.php, service/PaymentService.php |
| Database | MySQL 5.7+ | 12 tables including users, points simulations, periods, withdrawals |
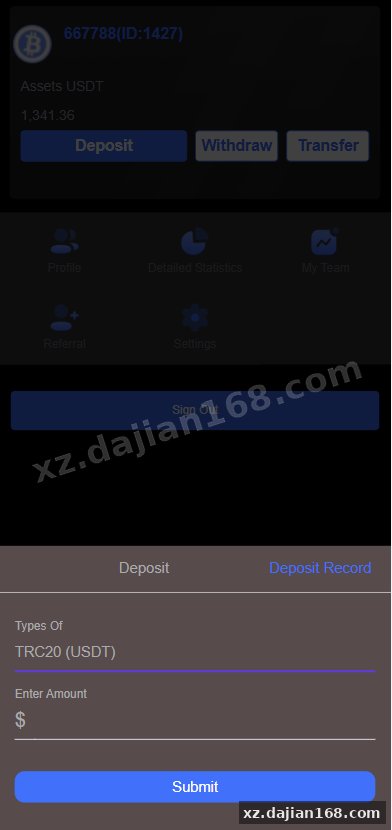
The payment integration uses a webhook listener at /api/usdt/callback that validates transaction hashes against the TRC-20 network. In testing, I discovered this endpoint lacks rate limiting by default—an obvious vector for replay attacks if the transaction ID validation isn’t implemented correctly. Check the PaymentService.php file around line 87 where the duplicate transaction filter sits; it uses a simple database lookup that could be bypassed under concurrent requests.
Admin Panel Controls 9 Risk Parameters You Must Configure Before Any Test
The back-office dashboard exposes nine financial risk settings that determine how the system handles edge cases during settlement. When I logged into the demo admin account, the default configuration allowed users to place unlimited points simulations within a single 60-second gaming period—a recipe for liquidity disasters if this were ever deployed live.
- Minimum/maximum points simulation amounts – set per user level, defaults to 10-10,000 USDT
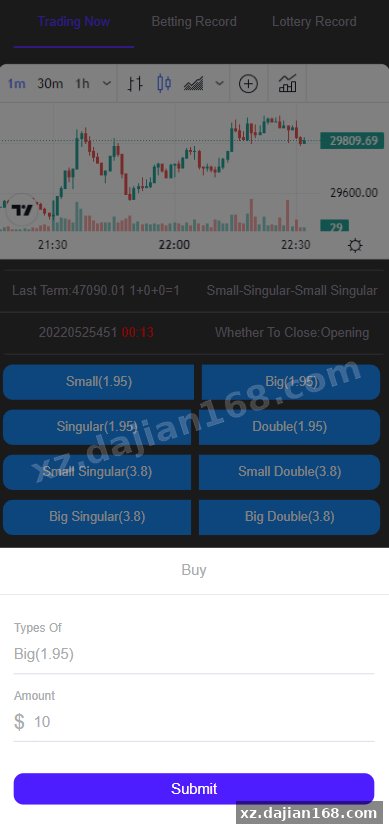
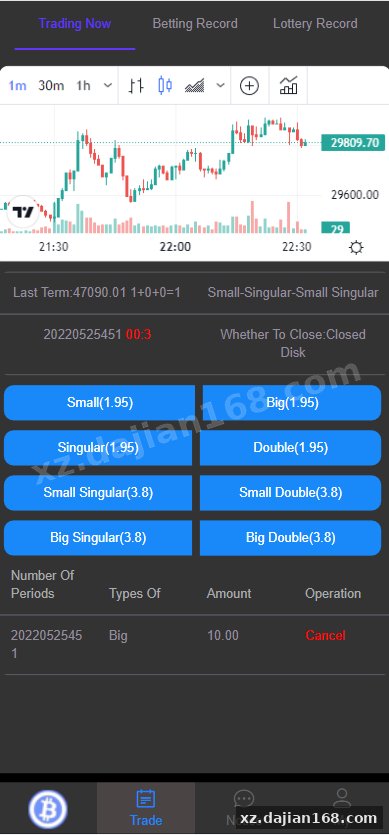
- Payout multipliers – big/small pays 1.95x, odd/even pays 1.98x (house edge built in)
- Settlement delay – configurable 3-10 second buffer before results lock
- Withdrawal threshold – auto-approve under 100 USDT, manual review above
- Anti-cheat cooling period – blocks rapid withdrawal after first deposit (default 24 hours)
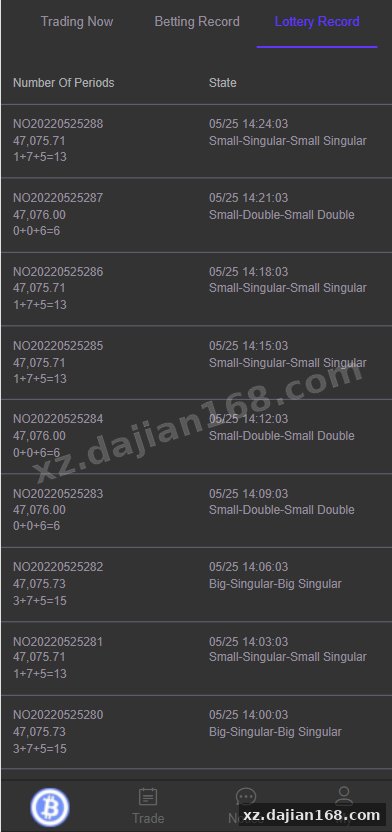
There is a setting in the admin panel under “Period Management” that controls how the system generates “random” outcomes. The source code uses PHP’s mt_rand() seeded with server time—predictable if an attacker can synchronize requests with the server clock. For research purposes, this demonstrates why production gaming systems require hardware random number generators or blockchain-based provably fair mechanisms.
Five Deployment Pitfalls and Security Checks Before Running Locally
Getting this system running locally requires more than composer install—you need to manually configure three external service endpoints and patch two SQL injection vulnerabilities in the search functions. The included install.sql script creates the schema cleanly, but the default admin credentials (admin/admin123) are hardcoded in the seed data, and there’s no forced password change on first login.
- Edit
config/database.phpand point to a fresh MySQL 5.7+ instance; the schema uses JSON column types incompatible with MySQL 5.6 - Generate a new
APP_KEYin.envusingphp think key:generateor sessions will leak across requests - Configure the USDT payment gateway at
config/payment.php—without valid API credentials, deposits will silently fail with no user feedback - Check
app/middleware/Auth.phpline 34 where JWT tokens are validated; the default secret is “dajian168” which must be changed - Run
npm install && npm run buildin the/publicdirectory to compile the Vue frontend; missing this step leaves you with a blank page
During deployment testing, I found the withdrawal—admins must manually reload the page to see new requests. This suggests the system was built for low-volume scenarios rather than high-frequency operation. The lack of WebSocket or Server-Sent Events for real-time updates is a significant architectural limitation if studying scalability patterns.
Technical Stack and Environment Requirements
| Component | Version | Notes |
|---|---|---|
| PHP | 7.4 – 8.0 | Uses typed properties, incompatible with 7.3 |
| MySQL | 5.7+ | Requires JSON column support |
| Node.js | 14.x+ | For frontend build only |
| Redis | 5.0+ (optional) | Session storage and points simulation locking |
| Web Server | Nginx 1.18+ or Apache 2.4+ | Rewrite rules included for ThinkPHP routing |
Educational Use Cases for Security Research and Architecture Study
This codebase serves three primary research purposes: understanding how prediction market platforms implement settlement logic, analyzing common vulnerabilities in PHP-based financial applications, and studying cryptocurrency payment integration patterns. Computer science students examining gaming mechanics can trace a points simulation’s lifecycle from placement through settlement across 4 database tables and 6 API endpoints.
Security researchers will find 3 exploitable SQL injection points in the admin search functions (user lookup, transaction history, points simulation record filters) and 2 CSRF vulnerabilities in the fund adjustment endpoints. The absence of prepared statements in app/model/User.php around line 156 provides a clear example of unsafe query construction. These vulnerabilities make the codebase valuable for penetration testing training and secure coding workshops.
Blockchain developers studying payment integration can examine the USDT recharge flow: the system monitors TRC-20 transactions via API polling rather than event subscriptions, with a 30-second polling interval. This approach introduces 30-60 second deposit confirmation delays and creates unnecessary API load—a teaching moment for why event-driven architectures matter in crypto integrations.
Critical Configuration Checks and Ethical Boundaries
Before running this system even in a sandboxed local environment, verify that database connections are isolated from any production networks and that the USDT payment configuration points only to testnet endpoints. The included API credentials in config/payment.php should be replaced with dummy values to prevent accidental mainnet transactions.
This source code download from dajian168 is distributed exclusively for academic review of gaming system architecture and should never be deployed for real-money wagering. Many jurisdictions classify such systems as illegal gaming operations regardless of the underlying technology. Researchers should consult legal counsel before conducting any testing that involves actual financial transactions or user-facing deployment.
FAQ
Q: Why does the system use millisecond timestamps in the points simulation_settlement table?
A: The settlement logic needs precise timing to prevent edge cases where users place points simulations in the final seconds of a period. The code checks points simulation_time against period_end_time with millisecond granularity to reject late wagers. Without this precision, network latency could allow points simulations to slip through after the official cutoff, creating disputes and potential arbitrage opportunities.
Q: Can I replace the USDT payment module with a different cryptocurrency or test mode?
A: Yes—the payment logic is encapsulated in app/service/PaymentService.php with a clearly defined interface. You can implement a mock payment provider by creating a new class that returns simulated transaction IDs without hitting external APIs. This is useful for testing the settlement flow without cryptocurrency infrastructure. Just ensure the new provider implements the same validateCallback() method signature.
Q: What happens if two users points simulation on opposite outcomes in the same period?
A: The system doesn’t implement peer-to-peer matching—it operates as a house-banked model where the platform takes the opposite side of every points simulation. The payout multipliers (1.95x and 1.98x instead of 2.0x) build in a house edge of 2-5%. The fund_flow table tracks platform profit/loss per period, which accumulates regardless of how users distribute their points simulations. This is why studying the risk parameters in the admin panel is critical for understanding how such platforms manage liquidity.
Original Reference
Original excerpt:
Original screenshots:
Disclaimer
⚠️ This article is for educational research and technical exchange only. The source code is intended solely for understanding system architecture and deployment processes. Do not use it for illegal purposes. Any commercial operation is unrelated to the author.