Contact Information: To prevent loss, please remember this website: dajian168.com Telegram: @dajian168 Telegram Channel: @dajian168168 WhatsApp: +852 Line ID: dajian168 Skype: [email protected] Email: [email protected] [email protected] USDT-TRC20 Address: USDT-TRC20 Address 2: Avatar/Profile:...
- About Us
- 2024-06-29
- 2247
A practical walkthrough on deploying an international short video and social content distribution platform using a UniApp frontend and ThinkPHP backend, covering i18n localization, video preloading, and user graph synchronization....
- Development Case Studies
- 2026-10-23
- 10
A hands-on walkthrough for building a social content distribution platform using a UniApp frontend and ThinkPHP backend. Covers video stream preloading, recommendation algorithm tuning, and multi-language customization tips....
- Development Case Studies
- 2026-10-23
- 8
Explore the complete deployment workflow for a lightweight, multi-language live chat system. This guide covers IP-based passwordless session tracking, WebSocket real-time state monitoring, and practical custom development tips for auto-reply bots....
- Development Case Studies
- 2026-10-23
- 6
【Urgent Security Alert】Remediation Guide for the PHP2Shell (CVSS 9.2) Critical RCE Vulnerability Dear customers: Hello! We are issuing the highest-level security alert regarding a serious security vulnerability in PHP core that is scheduled to be publicly disclosed at 22:00 Beijing time on October 21 (Wednesday). According to the international security organization Sansec, the recently surfaced vulnerability is known as PHP2Shell. Screenshots of automated exploitation tools for this vulnerability have already been leaked in the security community, and large-scale indiscriminate scanning and attacks are expected to begin across the internet within 15 minutes of the official patch release. Key Vulnerability DetailsVulnerability code/ID: PHP2Shell (CVE-2026-109618, CVE-2026-109619) Severity: CVSS 9.2 (Critical) Vulnerability type: Remote code execution (RCE); attackers can directly take over the server and gain shell access. Affected versions: All PHP versions from 5.4 onward. E-commerce systems such as Magento, Shopware, and WooCommerce, as well as various CMSs, will face severe threats. Patch release time: 22:00 Beijing time on October 21 (Wednesday) (14:00 UTC) ⚠️ Critical warning: No defense at the code levelThis vulnerability exists in PHP’s underlying architecture. This means that no code-level modifications, control panel hardening, or conventional application-layer protection plugins can block this attack. The only effective defense is......
- Development Case Studies
- 2026-10-23
- 8
【紧急安全预警】关于 PHP2Shell (CVSS 9.2) 核心级 RCE 漏洞的修复指南 尊敬的客户: 您好!针对即将在北京时间 10 月 21 日(周三)22:00 公开的 PHP 核心严重安全漏洞,我们在此向您发布最高级别的安全预警。 据国际安全机构 Sansec 披露,此次爆发的漏洞被称为 PHP2Shell。目前该漏洞的自动化利用工具截图已在安全社区泄露,预计官方补丁发布后 15 分钟内,全网将出现大规模的无差别扫描与攻击。 漏洞核心情报漏洞代号/编号: PHP2Shell (CVE-2026-109618, CVE-2026-109619) 危险等级: CVSS 9.2(极度危险) 漏洞类型: 远程代码执行(RCE),攻击者可直接接管服务器获取 Shell。 受影响版本: PHP 5.4 及以上所有版本。Magento、Shopware、WooCommerce 等电商系统及各类 CMS 将受严重威胁。 补丁发布时间: 北京时间 10 月 21 日(周三)22:00(14:00 UTC) ⚠️ 核心警告:无法在代码层防御该漏洞存在于 PHP 的底层架构中。这意味着任何代码级别的修改、面板加固或常规的应用层防护插件都无法拦截此攻击。防御的唯一有效方式是在服务器基础设施层面(环境底层)直接更新 PHP 版本。 紧急应对与修复建议官方将仅为 PHP 8.2、8.3、8.4 和 8.5 发布修复补丁。请您立即采取以下行动: 1. 正在使用 PHP 8.2 – 8.5 的用户(需今晚紧急操作): 随时待命: 请通知您的运维团队在今晚 22:00 前做好准备。 抢占黄金 15 分钟: 补丁一旦发布,请务必在第一波自动化攻击到来前,通过包管理器(apt/yum)或重新编译升级 PHP,并立刻重启相关服务(Nginx/Apache/PHP-FPM)。 2. 正在使用 PHP 8.1 及以下旧版本(含 5.6、7.x 等)的用户: 官方已明确不会为这些版本发布补丁。继续使用这些版本将让您的服务器完全裸露在 PHP2Shell 的攻击火力之下。 短期缓解: 立即排查并收紧服务器安全组及防火墙(iptables/firewalld)策略,开启高级别 WAF,并在 php.ini 中禁用高风险命令执行函数。 长期建议: 请即刻安排业务环境迁移,将底层升级至受官方支持的 PHP 8.2+ 版本。...
- Latest Updates
- 2026-10-22
- 24
A complete deployment walkthrough for a short video content delivery and multi-language H5 instant messaging system, covering WebSocket persistent connection setup, video feed recommendation logic, and frontend customization....
- Development Case Studies
- 2026-10-22
- 34
Practical deployment notes for a ThinkPHP-based short video distribution and social messaging system, covering video stream caching, recommendation algorithm setup, multi-language switching, and server environment troubleshooting....
- Development Case Studies
- 2026-10-22
- 32
A hands-on walkthrough of deploying a full open-source Java web-based instant messaging session management system, covering SpringBoot backend configuration, high-concurrency WebSocket tuning, and QR code authorization integration....
- Development Case Studies
- 2026-10-22
- 40
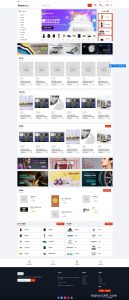
A hands-on deployment log for a Laravel-based multi-language cross-border e-commerce mall, covering one-click product collection and listing, merchant commissions, and payment integration experience....
- Development Case Studies
- 2026-10-21
- 58
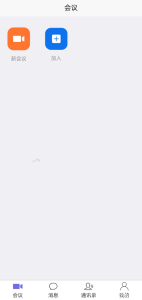
A hands-on record of deploying a screen sharing meeting system from source code, covering uniapp frontend packaging, PHP backend configuration, and lessons learned integrating the Tencent Cloud meeting SDK....
- Development Case Studies
- 2026-10-21
- 60