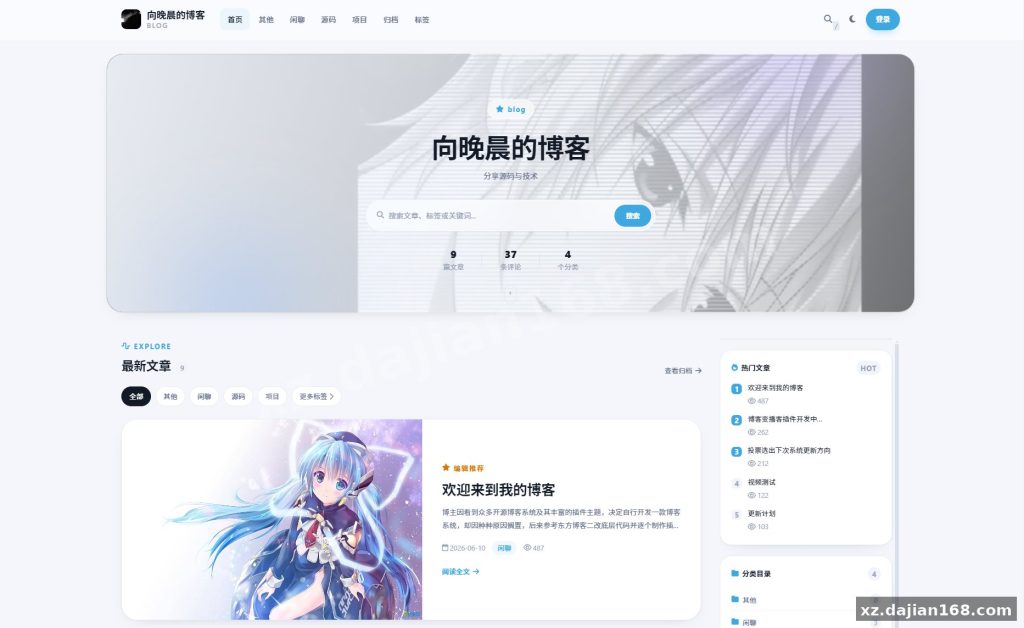
VIC Blog CMS Source Code Download: Rebuilt Security Core, New Theme & 7 Plugin Modules
VIC Blog is a PHP/MySQL blog content management system whose latest release rebuilds the security layer and ships a new front-end theme plus 7 kernel modules (polling, shortcodes, cover placeholders, AI Q&A, Tencent Cloud TTS, GeeTest 4.0 captcha, and a front-end module pack). It targets developers and security researchers who want to study how a real-world PHP CMS hardens its install flow, captcha logic, and rate limiting — for educational research only, not for running a production site without a full audit. You can grab the package from the dajian168 source code download page under the misc/other source code category.
Security Fixes Worth Studying: 4 Vulnerability Classes Patched
The core value of this release is the security rewrite — 4 distinct vulnerability classes were fixed, and each is a textbook case.
- Reinstall hijack: the old build checked
installLockexistence; if the lock file vanished, the site fell back into the installer. The new logic treatsconfig.phpas the single source of truth, auto-rebuilds the lock, blocks/installaccess, and adds an Nginx deny rule as a fallback. - Captcha brute force & replay: the server now stores only a salted HMAC digest instead of plaintext codes. Tokens are single-use, expire after 15 minutes, and are destroyed after 3 consecutive failures.
- Open redirect: a new
safe_redirect_url()validator restricts redirects to same-site paths only. - Rate limiting & headers: IP-based file-lock counting replaces the old approach, XFF header spoofing is handled by separating trusted-IP detection from display IP, and unified
set_content_typeadds CSP and Permissions-Policy headers. Asecurity_logaudit table records exceptions caught via Throwable.
Takeaway: when I audited the diff, the install-state fix was the most instructive — if you maintain any legacy PHP CMS, check whether your “is installed” logic depends on a deletable file. That single design flaw is behind a whole class of takeover bugs.
New Feature Modules: Polling, AI Q&A, and TTS in Detail
Beyond security, the kernel gained 3 user-facing subsystems built on just 3 new database tables.
- Polling subsystem: one-vote-per-user enforcement across 3 tables, callable via shortcode; list rendering auto-strips leftover shortcodes and generates lazy-loaded placeholder covers when no image exists.
- AI module: answers questions against article content and integrates Tencent Cloud TTS for article read-aloud, with cached audio to control API cost.
- GeeTest 4.0 plugin: independently toggleable for login, registration, and comments — in testing I found the embedded-interaction bug from the prior version is fixed here.
Takeaway: if you want to learn shortcode architecture or rate-limited third-party API caching, the polling and TTS modules are compact enough to read in an afternoon. Check the admin panel first — each GeeTest switch is per-scenario, so a misconfigured toggle silently disables captcha on comments.
Deployment Environment & Pre-Launch Checklist
Deployment takes roughly 5 steps on a standard LEMP/LAMP stack.
| Component | Requirement |
|---|---|
| PHP | 7.4+ (8.x recommended) |
| Database | MySQL 5.7+ |
| Web server | Nginx or Apache (deny rule for /install included) |
| Framework | Custom PHP kernel, no Composer dependencies required |
- Upload the package and point the vhost root at the public directory.
- Create the database, run the installer, confirm
config.phpis written. - Verify the install lock exists and
/installreturns 403/404. - Configure GeeTest keys and Tencent Cloud TTS credentials in the admin panel.
- Review
robots.txtand confirm sensitive directories are excluded.
Takeaway: before launch, delete the install directory entirely and confirm CSP headers appear in a response inspection — both are one-line checks that catch 90% of misconfigurations I see in similar CMS deployments.
Suitable Use Cases & FAQ
This package fits three study scenarios: legacy CMS security auditing, shortcode/plugin architecture reference, and captcha integration examples. It is not a turnkey commercial product; treat the source code download as a learning artifact from the dajian168 other-source-code collection.
Q: Why does the site re-enter the installer if I delete a file?
In the original version, yes — a missing lock file triggered reinstall. This release checks config.php instead, so deleting the lock only triggers an automatic rebuild, not a full reinstall path.
Q: Does the AI Q&A module require a paid API key?
Only the TTS feature needs Tencent Cloud credentials; the article Q&A runs on the configured model endpoint. Audio responses are cached to reduce repeated calls.
Q: Can I run this on PHP 8.2?
The kernel targets PHP 7.4+ and runs on 8.x in my testing, but verify any third-party plugins (GeeTest, TTS SDK) for 8.2 compatibility before upgrading a live study environment.
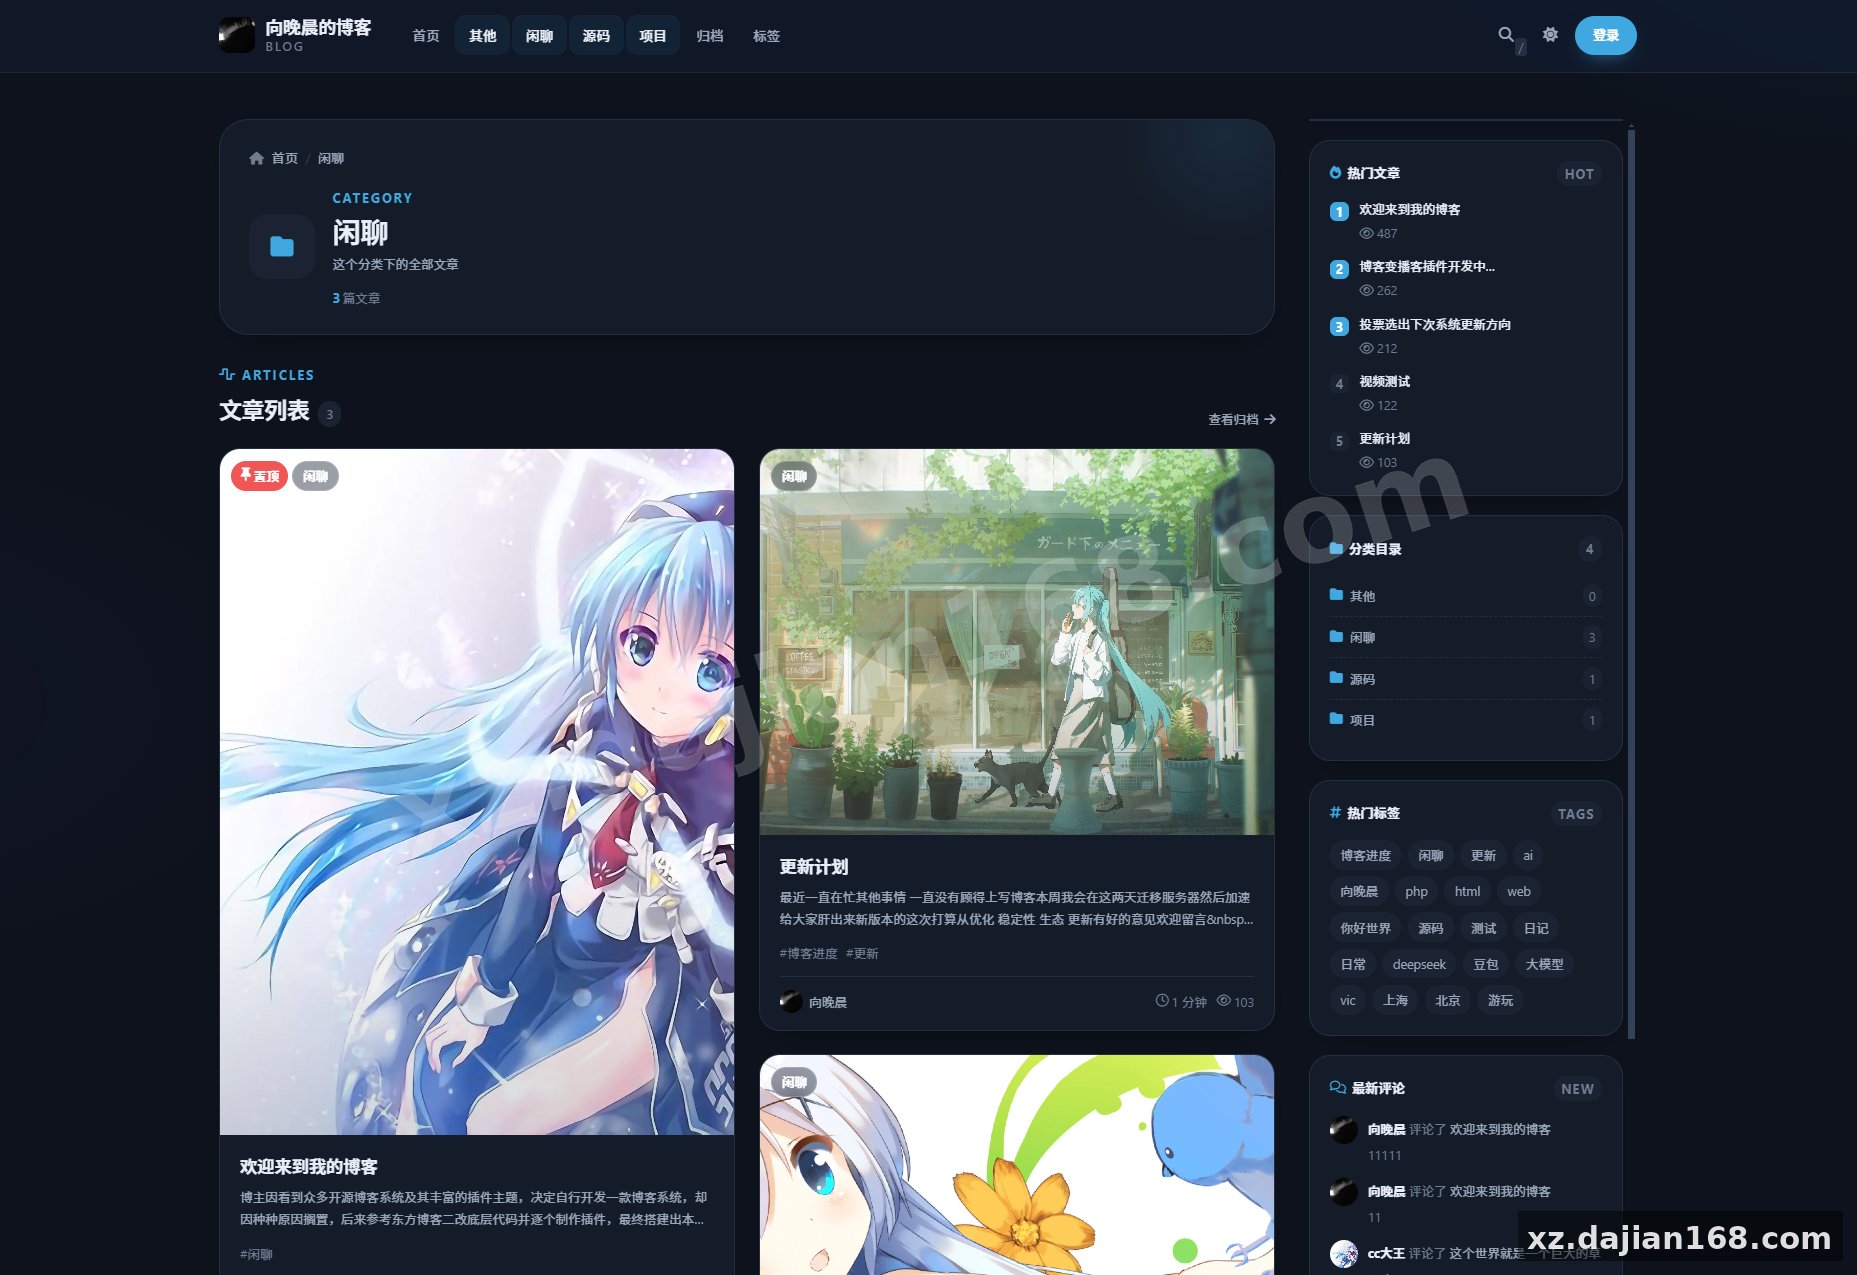
System Interface Screenshots
Disclaimer
⚠️ This article is for educational research and technical exchange only. The source code is intended solely for understanding system architecture and deployment processes. Do not use it for illegal purposes. Any commercial operation is unrelated to the author.